Current version2.0.0-RC7
2.0.0-RC7
Security: Implemented |e('js') Twig filters and U_ prefix standardization for all JS variables.
Security: Added explicit (int) casting to all database IDs and pagination variables to prevent SQL injection.
Security: Enforced SSL/TLS best practices for external socket connections.
Refactor: Removed legacy TRUNCATE commands in favor of portable SQL DELETE statements.
Refactor: Migrated manual SQL string building to native $db->sql_build_array() for better reliability.
Refactor: Cleaned up class constructors by moving logic/language loading to execution methods.
Refactor: Decoupled JavaScript from PHP controllers, moving inline logic to template files.
Fix: Resolved 'controller_helper::url' method error by migrating to the Symfony 'route' system.
Privacy: Disabled unverified guest email notifications to comply with GDPR/anti-spam policies.
Cleanup: Removed legacy 'ernadoo' vendor references in routing and language calls.
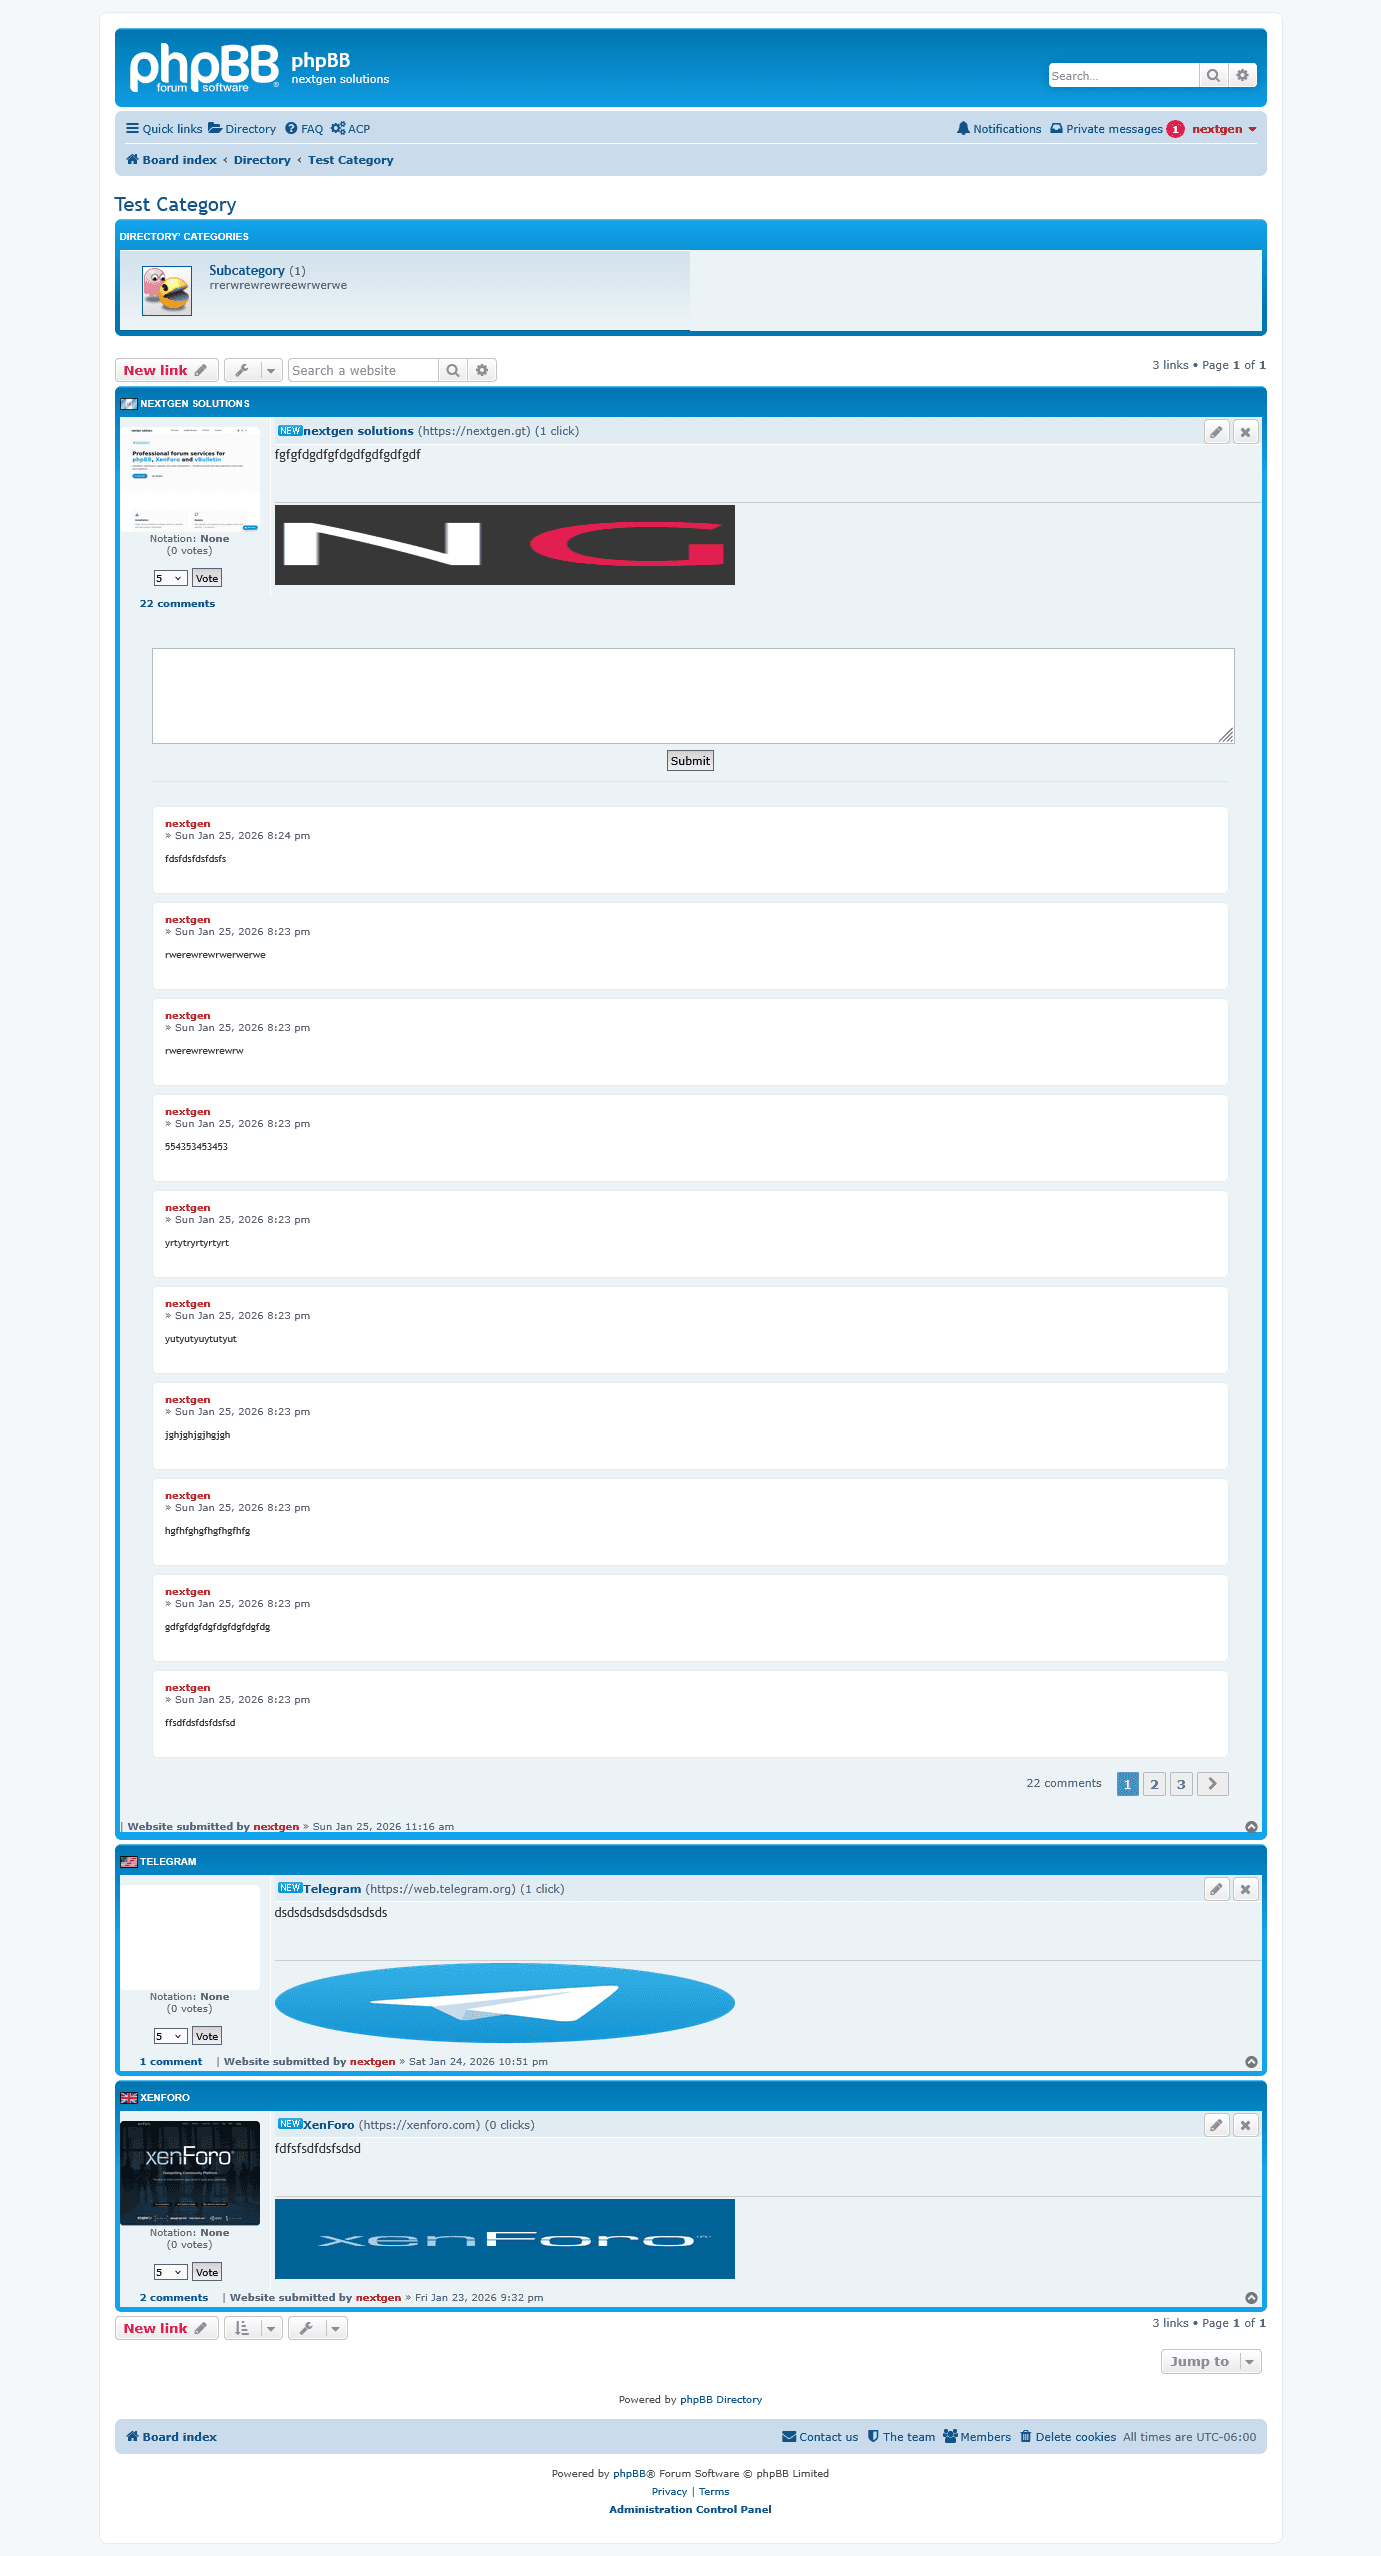
Refactor: Decoupled thumbnail HTML generation from search controller to template.
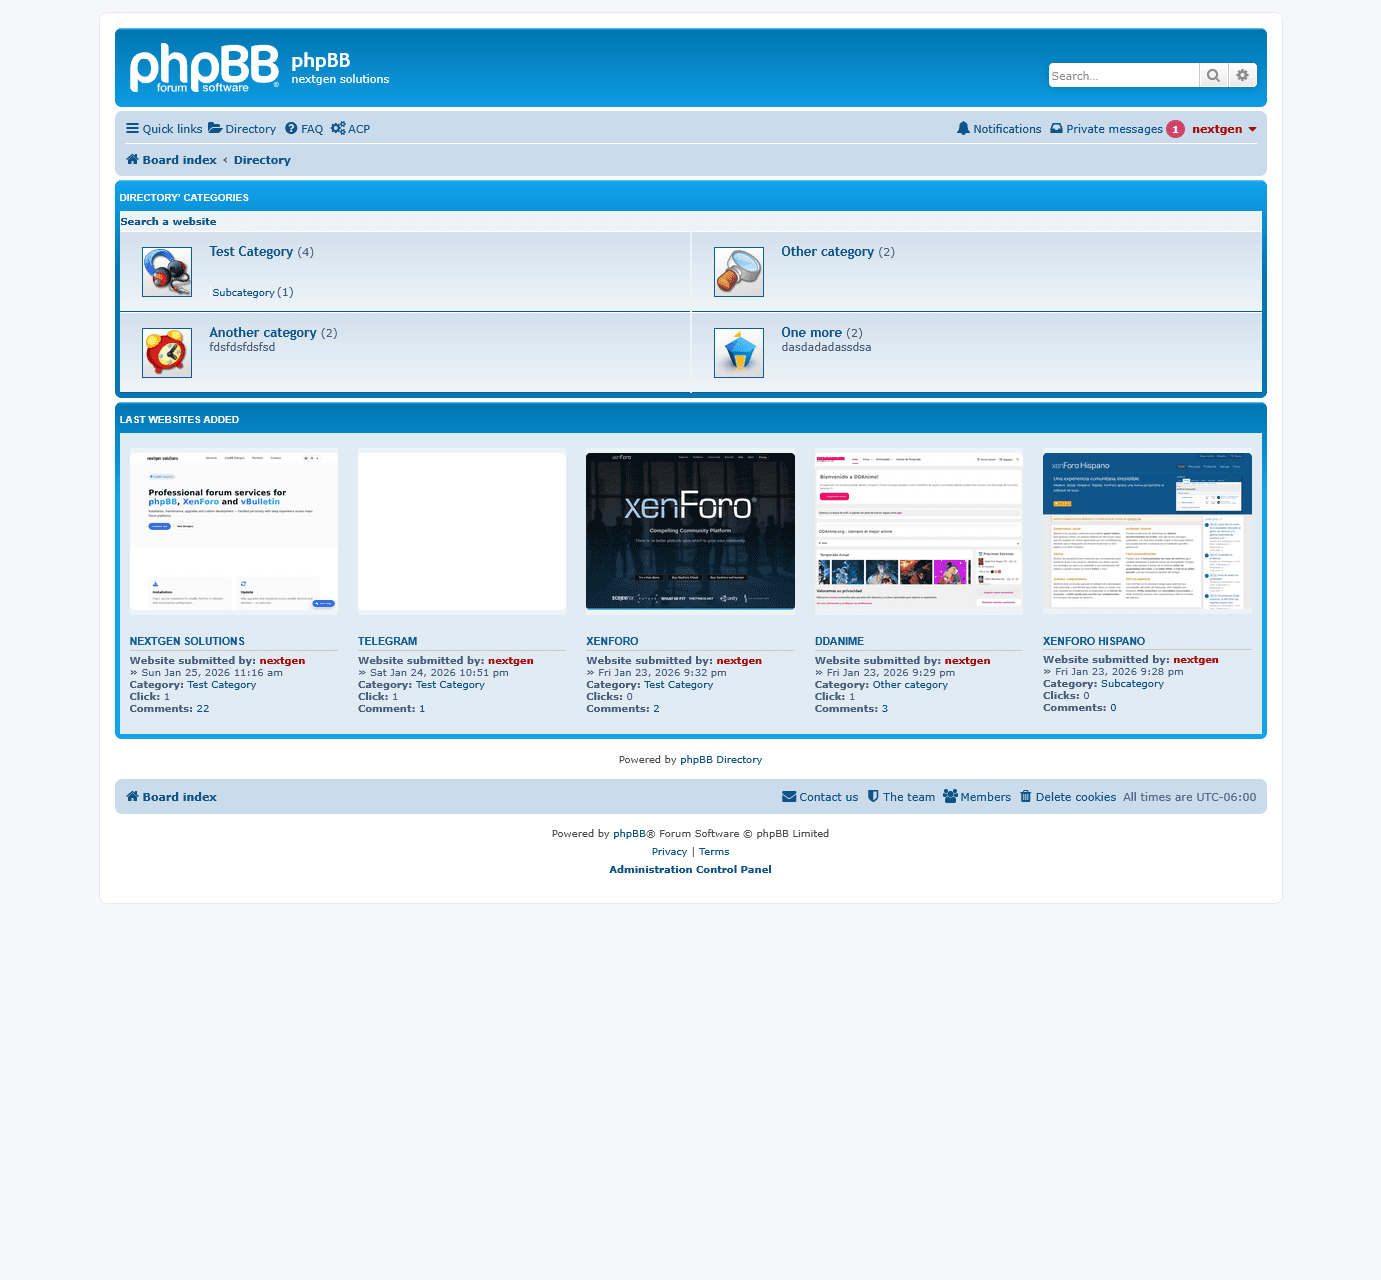
Fix: Resolved syntax error in search results causing "/>" characters to display as text.
UI: Improved search results layout with min-height constraints and responsive thumbnail scaling.
Security: Replaced raw HTML output with secure Twig variables for site names and image URLs.
Bump version to 2.0.0-RC7 in composer.json.
Comments
Comments are powered by GitHub Discussions. A GitHub account is required to participate.